Given that most operate in highly complex IT environments with hundreds if not thousands of users, applications, and services all needing privileged access, least privilege must be treated as an ongoing program, not a one-time cybersecurity project. It’s the only way to truly protect against internal and third-party threats and meet compliance mandates.
Least privilege, therefore, requires a multi-technology, multi-discipline approach. One that involves IT and security stakeholders collaborating with all parts of the organization. It should be supported by an executive who is responsible for security—CISO or VP-level security executive—who serves as the final decision maker, approves staff roles, and ensures an adequate budget is allocated.
The report recommends designating a “least privilege champion”—someone who recognizes the need for the program and solutions being implemented and who has a general security role with responsibility for identity and access management. This champion should also be the point person to communicate and coordinate with other influencers and stakeholders in the process, such as network security, application security, and other endpoint-related departments.
Conclusion: one size does not fit all
At a time when we are experiencing a record number of people required to work remotely, it’s imperative that organizations use all the tools at their disposal to enforce least privilege while maintaining user productivity.
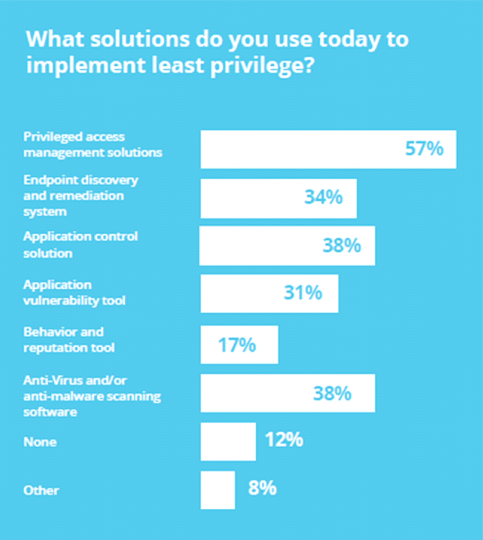
Effective implementation of least privilege, especially on endpoints, requires multiple layers of protection. Existing solutions can and should be used in conjunction with a PAM product that provides least privilege-specific capabilities. Integration of these tools is necessary to help automate the task of ongoing management of a least privilege program. For example, your application control solution should connect to your IT help desk ticketing system, and work in conjunction with a vulnerability scanner.
There is no one product or one company that will meet all organizational needs for least privilege. A defense-in-depth strategy is key, in addition to integrating products that complement each other.
To see the survey results, get key takeaways and recommendations along with free resources, download the free 2021 Global State of Least Privilege Cybersecurity report here.