-
Accelerate AI SecurelyEnable secure AI adoption with visibility, governance, and control across identities, agents, and accessDefend Against AI AttacksProtect your organization from AI-driven threats by securing identities, controlling access, and reducing attack paths.Cyber InsuranceImprove your cyber insurance readiness with stronger identity security, governance, and privileged access controls.RansomwareDefend against ransomware by securing privileged identities, limiting access, and reducing attack paths.Vendor ConsolidationReduce complexity, strengthen security and improve IT ROI through platform consolidation.Secure Remote WorkforceSecure access for employees, contractors, and third parties from anywhere.Reduce Identity RiskGain visibility, control, and continuous authorization across every identity.Financial ServicesReduce identity risk and strengthen governance across financial institutions.HealthcareSecure access to critical systems, patient data, and clinical environments.Federal & PublicSupport secure access, compliance, and operational resilience across public sector enterprises.Energies & Critical InfrastructureProtect critical systems and privileged access across essential infrastructure.EducationProtect your educational institution from ransomware and data misuse.VisibilityDiscover every human, machine, and AI identity across your environment.PostureIdentify excessive privileges, policy gaps, and emerging identity risks.ControlApply authorization and access policies to every identity, session, and action.Human IdentitiesSecure workforce, privileged, and third-party identities.Machine IdentitiesProtect secrets, credentials, certificates, and non-human identities.Agentic IdentitiesGovern and control access for AI agents and autonomous systems.Cloud StatusCheck availability and service health across Delinea cloud services.Customer SupportGet product support, technical guidance, and help from Delinea experts.Identity Security Maturity ModelAssess your identity security maturity and identify priorities for improvement.Professional ServicesAccelerate deployment, adoption, and value with expert implementation and advisory services.Trust CenterAccess Delinea security, privacy, compliance, and assurance information.User TrainingBuild product knowledge and skills with Delinea training and learning resources.
-
The Delinea PlatformA unified identity security platform that protects human, machine and AI identities across your enterprise.Delinea Iris AIAI-powered intelligence that delivers real-time insights, automation and continuous authorization.Secret ServerSecure privileged credentials with enterprise password vaulting and session management.Continuous Identity DiscoveryContinuously discover and inventory every identity across your enterprise.Credential ManagerManage, rotate and protect privileged credentials across hybrid and cloud environments.Fastpath Access GovernanceAutomate access governance, segregation of duties and compliance reporting.Privilege Control for ServersEnforce least privilege and application control across Windows and Linux servers.Privileged Remote AccessProvide secure remote access for employees and third parties without exposing privileged credentialsFull Product ListingBrowse the complete Delinea product portfolio and find the right solution for your enterprise.Why Delinea FastpathDiscover how Delinea Fastpath helps enterprises govern access, reduce risk and strengthen compliance across critical business applications.Delinea Fastpath Access ControlIdentify Segregation of Duties conflicts and sensitive access risk within and across business applications.Delinea Fastpath Access ReviewAutomate user access reviews and generate clear, consistent audit evidence with less manual effort.Delinea Fastpath Change TrackingMonitor critical permission, configuration and data changes across business applications.Delinea Fastpath Access ProvisioningAutomate compliant access requests, approvals, provisioning and deprovisioning.Delinea vs CyberArkCompare Delinea and CyberArk to see how the platforms differ in identity security, deployment and ease of use.Delinea vs BeyondTrustExplore the key differences between Delinea and BeyondTrust across privileged access and identity security.Delinea vs MicrosoftSee how Delinea extends beyond native Microsoft capabilities to deliver comprehensive identity security.Delinea vs One IdentitySee how Delinea authorizes every action at runtime, keeps credentials off users and AI agents and supports your identity provider.Delinea vs SaviyntExplore how Delinea and Saviynt compare across identity security, governance and privileged access.
-
All ResourcesBrowse Delinea’s complete library of educational content and resources.BlogsStay up to date with the latest identity security insights and industry trends.VideosWatch product demonstrations, customer stories and educational content.WebinarsJoin expert-led webinars covering identity security and best practices.EventsDiscover upcoming conferences, webinars and Delinea events.EbooksDownload in-depth guides, research and educational resources.GlossaryUnderstand key identity security, cybersecurity, and privileged access terms with Delinea’s comprehensive glossary.PodcastEnjoy freshly brewed hot takes with our Grounds for Access podcast.Product DocumentationAccess technical guides, product documentation, and implementation resources.Solution BriefsLearn how Delinea solutions address specific business and security challenges.Trust CenterReview security, compliance, privacy, and trust-related information.
-
Customer SuccessMaximize the value of your Delinea investment with expert guidance and ongoing success planning.Professional ServicesAccelerate deployment and optimize your identity security strategy with Delinea experts.User TrainingBuild product knowledge and develop expertise through Delinea training and certification programs.Cloud StatusView the real-time status and availability of Delinea cloud services.Customer CommunityConnect with peers, share knowledge and discover best practices from the Delinea community.Integrations MarketplaceExplore integrations that extend and enhance the Delinea Platform across your technology ecosystem.Product DocumentationAccess technical documentation, product guides, APIs and implementation resources.Technical SupportGet expert assistance, troubleshoot issues and manage support requests.Trust CenterReview Delinea’s security, compliance, privacy and trust information.
-
About DelineaLearn about Delinea’s mission, vision, and approach to identity security.The Delinea DifferenceDiscover what sets Delinea apart in securing human, machine, and AI identities.Leadership TeamMeet the leaders driving Delinea’s strategy and innovation.Contact UsConnect with our teams around the world.
What is a non-human identity?
Why NHIs matter to SecOps
 NHIs are a major concern for today’s security teams. According to a 2026 Cloud Security Alliance Report, NHIs outnumber human identities by an average of 45 to 1 across enterprises and 144 to 1 in cloud-native environments. Those ratios are likely to increase even further as agentic AI adoption proliferates.
NHIs typically authenticate using secrets such as tokens, keys, certificates and passwords, which are often hard-coded directly into applications or configuration files rather than stored in a managed vault. When that code or those files end up in a public repository like GitHub, the exposed credentials become easy prey for threat actors.
Adversaries routinely use compromised credentials to breach systems, traverse networks, exfiltrate data and carry out attacks. Credential abuse plays a role in 39% of breaches, according to a Verizon 2026 Data Breach Investigations Report. And many of those breaches involve NHIs.
NHIs are often over-permissioned and granted standing privileges, making them a favorite target for attackers. In fact, OWASP calls out excessive privileges as one of the top ten risks associated with non-human identities.
In a 2026 Delinea Identity Security Report, 73% of decision-makers agree that standing access for NHIs increases risk. But 68% say they often accept standing access for NHIs under operational pressure. Today, much of that operational pressure comes from agentic AI.
AI agents expand the attack surface
Agentic AI is transforming the NHI threat landscape. AI agents typically operate outside established identity and access controls. They often inherit excessive access privileges from a user's credentials or from a shared service account. Unlike human identities, AI agents operate at machine speed, making it difficult for security teams to identify and mitigate threats before they spread across the enterprise. In a 2026 IBM Institute for Business Value
survey, 77% of CIOs, CTOs and other technology leaders said that AI adoption is outpacing their organization's governance capabilities.
-
Standing access creates permanent exposure
Every identity with persistent, privileged access is a standing target. The credentials don't have to be actively in use for the risk to exist. A dormant service account, a CI/CD pipeline running on long-lived credentials or an AI agent granted broad permissions during deployment can all become entry points for an attacker.
According to the 2026 Delinea Identity Security Report, organizations are more than twice as likely to grant NHIs and AI agents long-lived credentials as they are to use just-in-time authorization. Only 8% of respondents said they use ephemeral credentials. -
Zero standing privilege is essential for agentic AI security
ZSP was originally applied to human administrators, but the most urgent need today is for AI agents. Unlike traditional automation scripts, which execute pre-programmed steps, AI agents can make contextual decisions at runtime. They can determine which systems to interact with, request additional access, invoke new tools and trigger privilege changes on their own. A single agent with standing privileges can move across multiple systems at machine speed, spreading damage far faster than security teams can detect and mitigate.
-
ZSP complements least privilege
Least privilege defines how much access an identity should have, while zero standing privilege adds a time dimension. An identity can hold a minimal set of permissions and still pose a risk if those permissions are always available. ZSP reduces that risk by requiring that access not persist indefinitely.
-
Zero standing privilege reduces the blast radius of a breach
No security program can completely eliminate credential theft and abuse. Users can still fall for clever phishing attacks. And disgruntled employees can still share credentials with threat actors.
Zero standing privilege limits what an attacker can do with a compromised credential once they have it. It reduces the blast radius, limiting a threat actor's ability to move laterally and expand the scope of an attack. When an account holds no standing privileges, a stolen credential is of limited value.
The anatomy of an NHI
Every NHI consists of two components: an identifier and a credential. The identifier uniquely represents a machine, application, workload or service. The credential authenticates that identity and may take the form of a password, API key, certificate, token or another authentication mechanism. Together, they enable trusted machine-to-machine communication without human intervention.
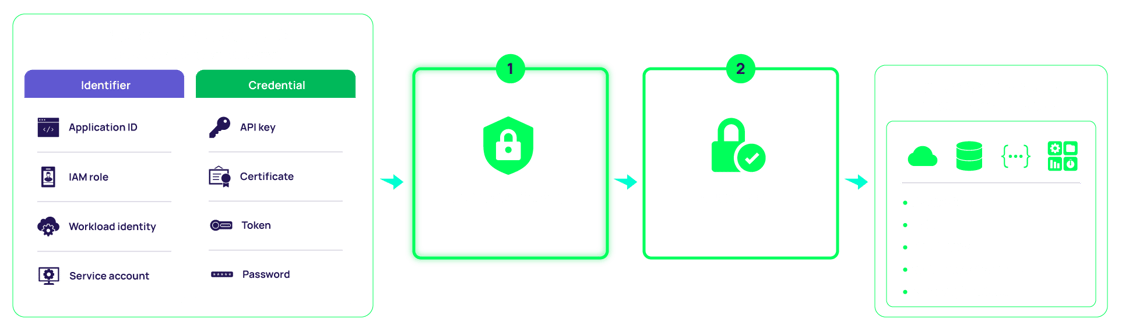
NHIs are used to authenticate and authorize access to enterprise resources
NHIs operate across nearly every layer of modern IT. They are used to run background jobs through service accounts, to exchange data between microservices and databases, to deploy infrastructure through CI/CD pipelines and to enable IoT devices, sensors and robotic process automation tools to execute functions and carry out tasks. Different types of NHIs are often created and managed by different teams, making consistent governance difficult.
NHI governance systems and practices
Most enterprises have formal workforce identity systems and practices for governing employees, contractors, vendors and other individuals. Identity teams use IAM and IGA tools to manage identities and access rights as people join the company, change roles or leave the organization.
Many enterprises don't have comparable systems in place for managing NHIs. In many organizations, NHIs are created manually by developers when building or deploying an application or an AI agent. They are often shared across applications without common oversight. Without a clear owner, an NHI can outlive its purpose unnoticed.
NHI governance solutions help organizations overcome these challenges by automating lifecycle management, centralizing administration and unifying visibility across the extended enterprise. They strengthen NHI security by bringing proven human identity governance practices to the world of non-human identities.
Common NHI governance capabilities
Capability |
Function |
Benefit |
Discovery and inventory |
Uncover NHIs scattered across the entire IT estate | Improve visibility and reduce exposure |
Credential vaulting |
Isolate, secure and rotate secrets |
Remove secrets from applications and configuration files |
Identity lifecycle management |
Automatically provision and deprovision identities and access rights |
Eliminate stale identities and standing access |
Threat analysis and response |
Continuously monitor NHI posture and flag anomalous behavior | Surface suspicious activity before attackers can do lasting damage |
-
NHI security and governance best practices
Effective NHI management begins with visibility and extends throughout the identity lifecycle. While every business has different requirements, these best practice recommendations can help any organization improve NHI governance and reduce risk. -
Discover every non-human identity
Governance begins with visibility. Continuously discover and inventory AI agents, service accounts, applications and other machine identities across your entire IT estate, including on-premise, cloud and SaaS platforms. A complete inventory provides the foundation for risk assessment and access control.
-
Centralize governance and ownership
Clearly define the owner responsible for approving access, reviewing permissions and retiring identities that are no longer needed. Centralized governance helps reduce orphaned identities, inconsistent policies and administrative blind spots.
-
Protect and rotate credentials
Replace hard-coded credentials with centrally managed secrets whenever possible. Rotate API keys, certificates, tokens and other credentials regularly and use short-lived credentials where supported to reduce the impact of credential theft.
-
Enforce least privilege
Grant every NHI only the minimum permissions required to perform its intended function. Regularly review and remove excessive permissions and replace standing privileged access with time-limited or task-specific access wherever practical.
-
Monitor identity activity
Continuously monitor authentication events, privileged activity and credential usage to identify anomalous behavior and contain threats before they spread across the enterprise.
Related security concepts
Many NHI security, governance and management concepts overlap with or complement other cybersecurity disciplines and solutions.
Concept/capability |
Function |
How it relates to NHI security |
Privileged Access Management (PAM) |
Vaults and rotates privileged account credentials and audits privileged account activity. | PAM solutions often manage a subset of NHIs, mainly service accounts with elevated access. Traditional PAM platforms can't meet the scalability and performance requirements of AI agents and other contemporary NHIs. |
Identity governance and administration (IGA) |
Manages identities and access rights across the lifecycle. |
Most traditional IGA solutions were originally designed to manage human identities. NHI governance solutions extend established lifecycle management practices to non-human identities. |
Secrets management |
Stores, rotates and injects the credentials NHIs use to authenticate. |
Secrets management protects the credential component of an NHI. |
Cloud infrastructure entitlement management (CIEM) |
Analyzes permissions across cloud providers to flag excessive or unused access. | Many CIEM solutions can surface over-permissioned NHIs. |
Zero standing privilege (ZSP) |
Ensures human and non-human identities are never granted permanent privileged access to critical enterprise resources. | ZSP is one of the primary goals of NHI governance. |
Machine identity management (MIM) |
Manages certificates, keys and other credentials tied to machines and workloads, often with a focus on cryptographic assets. | MIM and NHI security cover much of the same ground, though NHI security places more weight on ownership, behavior and lifecycle rather than certificate management. |