Identity security vendors – compare the differences

Delinea  vs. Britive


Britive governs the entitlement. Delinea stays for the session, authorizing every action before it runs.

Britive eliminates standing privilege across cloud IAM, SaaS apps, and AI agents but leaves a policy enforcement gap once a session with the infrastructure is open. Delinea closes the gap with runtime authorization.

Access control that doesn't stop at the grant

Britive provisions ephemeral entitlements directly through native cloud and SaaS APIs, with no proxy or agent in the connection and revokes them when a posture signal changes. Delinea treats that grant as the point where its job starts.

  • Delinea stays in the path for the life of the session across servers, databases and Kubernetes clusters, checking every command, query and tool call against policy before it runs rather than logging it after.
  • Delinea blocks and redacts specific actions, stopping a destructive SQL statement or redacting a sensitive column mid-session. This is available today on Postgres and Microsoft SQL Server, with more coverage on the roadmap.
  • No added friction for users. Engineers and agents keep the tools and workflows they already use.
  • Gateways and relays run redundantly with automatic failover, so the control plane doesn't go down if one node does.
delinea-photo-govern-access

Identity security built for the AI era

Delinea centralizes authorization across every AI agent, human and machine identity and enforces it at runtime.

  • The Delinea Gateway authorizes each tool call an AI agent makes before it executes. It’s live today for Claude Code, Claude Desktop, Codex CLI, GitHub Copilot in VS Code and Kiro.
  • Delinea authorizes the action itself against policy before it runs, brokering the connection and injecting the credential at the proxy so the person or agent never holds it.
  • Service accounts and pipelines get the same policy and audit treatment as human users.
delinea-photo-AI-tiles-shorter

Identity security vendors – compare the differences
Delinea Logo        
vs          
cyberark-idira-logo

Delinea delivers one platform built for the way modern enterprises actually run

Easier to implement - Easier to use – Easier to manage

The Delinea Platform serves both traditional PAM and modern workload-access buyers through one identity,
one policy, and one audit. CyberArk (now Idira) ties your choice of vault to Palo Alto Networks' broader SOC and security platform commitment.

The Delinea Platform reduces risk and simplifies operations

Delinea extends access control into continuous, runtime authorization across every AI, human and machine identity.

Compare the differences between Delinea and Britive

Capability

Delinea Logo

Britive

Traditional PAM buyer 


 In-session enforcement, human sessions 

delinea-icon-strong-purple
 Blocks and redacts live, Postgres and SQL Server today

delinea-icon-poor-purple
 No in-session presence; revokes at the entitlement layer on a posture signal 

 Session recording and audit evidence

delinea-icon-strong-purple
 Command-level replay, RDP video, structured logs 

delinea-icon-poor-purple
 No session to record; logs entitlement grants and revocations instead

Modern workload access buyer 


 Cloud IAM and SaaS entitlement provisioning

delinea-icon-good-purple-2
 Federated access to AWS, Azure, GCP consoles, not native role authoring 

delinea-icon-strong-purple
 Native JIT provisioning across AWS, Azure, GCP, OCI, and 100+ SaaS apps 

AI agent identity


  In-session enforcement, AI agent sessions 

delinea-icon-strong-purple
 Delinea Gateway authorizes every tool call live

delinea-icon-strong-purple
 MCP Gateway governs agent identity with human-in-the-loop approval at the entitlement layer

  Continuous enforcement model 

delinea-icon-strong-purple
 Continuous, per-action authorization for as long as a session is open   

delinea-icon-strong-purple
 Continuous, signal-based revocation via SSF/CAEP when device or risk posture changes 

Deployment and ecosystem 


 Resource and infrastructure coverage

delinea-icon-strong-purple
 47+ resource types across databases, servers, K8s, cloud, network devices, and web apps, all through one proxy model

good
 Cloud IAM, SaaS and non-human identity are the core model; servers and on-premise access run through a separate Access Broker component

 Trusted by real organizations   

"You don't even know [Delinea runtime authorization] StrongDM is there once it's installed. It just works. It's that simple."

"We used [Delinea] StrongDM to instantly deliver results to our auditors, which really simplified the SOC 2 process."

"The effort to achieve SOC 2 without [Delinea] StrongDM would have been monumental from a cost & labor perspective."

Why the differences between Delinea and CyberArk matter

delinea-icon-lightning

Faster to deploy: Easier to use

Delinea is consistently recognized for requiring fewer resources to manage and less time to achieve full functionality.

  • • 99.995% uptime SLA
  • • No multi-year commitment required to start
delinea-icon-just-in-time-teal

Zero standing privilege—available now

Delinea ships ephemeral access with proxy injection, JIT entitlement, and full session recording for human, machine, and AI agent identities - today.

  • • Native tools, broker invisible
  • • Time to value in weeks
delinea-icon-ai-agent-teal

Identity security built for the AI era

Delinea centralizes authorization with runtime enforcement across every AI agent in your stack.

  • • MCP-native connectivity
  • • Customers are using this in production today

Why the differences between Delinea and Britive matter

Governing the entitlement is not the same as controlling the session

Britive's job is to decide what gets granted and revoked at the cloud IAM or SaaS layer, cleanly, and without a proxy in the way. That doesn't cover what happens once the grant is live. 

  • Britive provisions the entitlement, then steps back. A posture signal is what brings it back into the picture, not the session itself. 
  • Delinea stays in the path for the life of the session, evaluating every command, query or tool call against policy before it runs. Britive can revoke access; Delinea can stop the action before it finishes.

Britive governs AI agents, but human privileged sessions work differently

Britive's MCP Gateway governs an AI agent as a distinct identity, with a registry and human-in-the-loop approval before it acts. Human privileged sessions work differently.

  • Britive's own materials describe something narrower for human sessions: entitlement provisioning and posture-based revocation, with no documented claim of blocking a specific action mid-session. 
  • Delinea blocks destructive SQL statements and redacts sensitive columns while a person's session is still live. This is available today on Postgres and Microsoft SQL Server.

Britive waits for a signal while Delinea is already in the session

Britive's model depends on another system noticing that a device looks compromised or a risk score moved before it can act. 

  • Britive waits for a posture signal from another system. Until that signal lands, the entitlement stays live and nothing inspects what the identity is doing with it.
  • Delinea checks every command against policy at the moment it runs and ties it to the individual identity behind it, whether that’s an engineer, service account or AI agent.

Thousands of customers. One easy choice.

Industry leaders and innovative disrupters agree: our PAM solutions are the easiest to try, buy, implement, and own.
With Delinea, privileged access is more accessible.
CISCO LogoExxonMobil LogoIBM LogoHarvard LogoHubSpot LogoBP Logo Zynga Logo  Macmillan LogoSAAB LogoValero LogoBeazley LogoUS Department of Defense SealJohnson & Johnson LogoNIST Logo

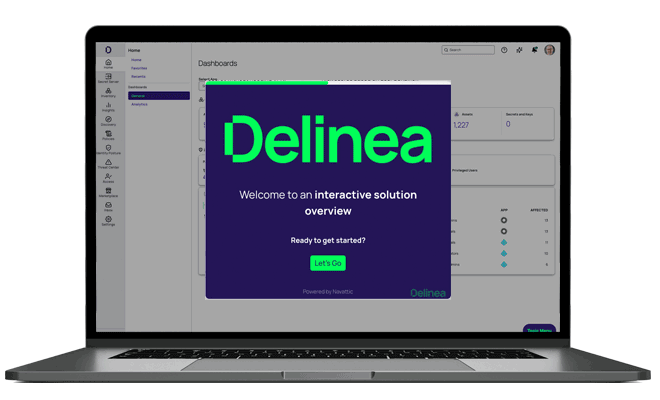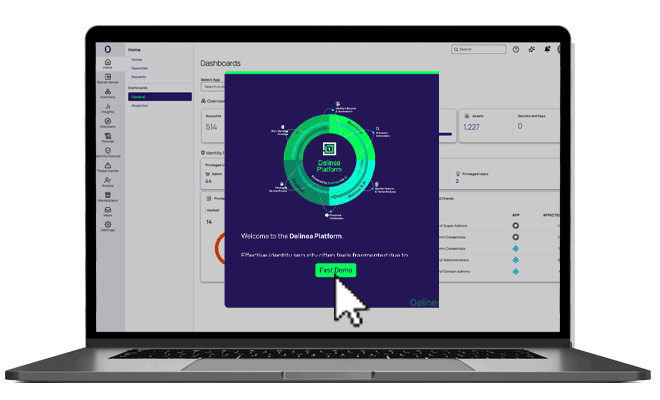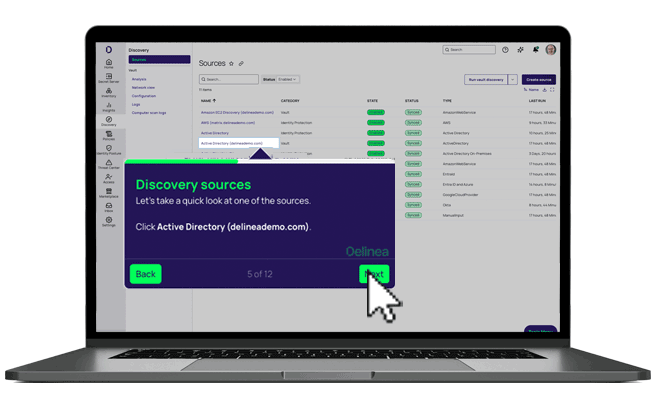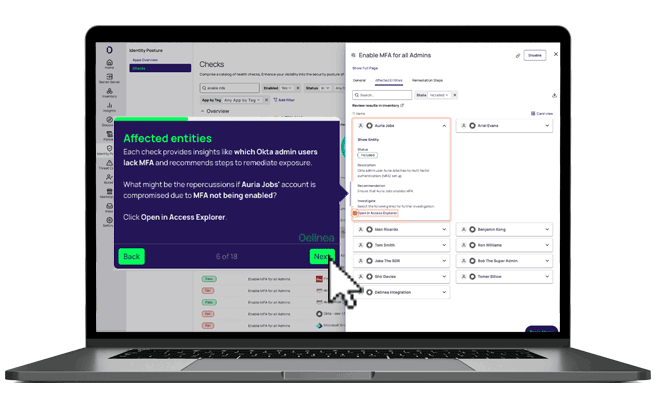
See the Platform in action

The Delinea Platform enforces policy at execution, reduces risk, simplifies operations, and ensures every action is authorized, auditable and defensible across every AI, human and machine identities.

Delinea Platform Demo Screen

Frequently Asked Questions

Can Delinea replace Britive, or does it just work alongside it?

Both. It depends on what you need to control. If you need to control and audit what happens during a session, block a destructive query, record it and authorize an AI agent's tool calls, Delinea covers that on its own, and you may not need Britive at all. If you need native, API-driven entitlement provisioning across cloud IAM and 100+ SaaS apps, Delinea runs alongside Britive instead, brokering and auditing sessions while Britive handles entitlements.

How does Delinea’s AI agent governance compare to Britive's MCP Gateway?

Both authorize agent actions rather than just logging them. The enforcement point is what differs. Britive governs the agent as a distinct identity, with a registry and human-in-the-loop approval at the entitlement layer. The Delinea Gateway enforces explicit per-tool-call policy live, ties every agent action into the same command-level audit trail as human and service account sessions, and never lets the agent hold a credential in the first place. 

Does Delinea provision native AWS, Azure, GCP or OCI IAM roles the way Britive does?

No. Delinea brokers the connection to a resource through a proxy rather than authoring native cloud IAM policy at the entitlement layer. For native cloud IAM policy authoring, Delinea sits alongside Britive rather than replacing it. A solutions engineer can map where the line falls in your environment.

Can Delinea govern SaaS entitlements across 100+ apps the way Britive does?

No. Britive provisions entitlements inside SaaS applications. Delinea gates access to SaaS and cloud resource types at the session layer, which is a different job. If you need SaaS entitlement governance at that breadth, the two run together. 

How does session recording compare?

Britive doesn't record sessions, since it isn't in the data path. Delinea provides command-level replay, RDP video and structured logs for as long as the session runs. That's one of the clearest differences between a control-plane model and a broker model.

If we're evaluating Britive today, what does adding or switching to Delinea involve?

It depends on whether you’re adding Delinea or switching to it. If you’re switching because session control is the priority, a solutions engineer discovers and onboards your infrastructure directly, including servers, databases, Kubernetes workloads, network devices and cloud consoles, with no requirement to have run Britive first. If you’re running both, that same onboarding happens in parallel with Britive's existing entitlement provisioning, and you can walk through how the two fit together for your environment.