-
Accelerate AI SecurelyEnable secure AI adoption with visibility, governance, and control across identities, agents, and accessDefend Against AI AttacksProtect your organization from AI-driven threats by securing identities, controlling access, and reducing attack paths.Cyber InsuranceImprove your cyber insurance readiness with stronger identity security, governance, and privileged access controls.RansomwareDefend against ransomware by securing privileged identities, limiting access, and reducing attack paths.Vendor ConsolidationReduce complexity, strengthen security and improve IT ROI through platform consolidation.Secure Remote WorkforceSecure access for employees, contractors, and third parties from anywhere.Reduce Identity RiskGain visibility, control, and continuous authorization across every identity.Financial ServicesReduce identity risk and strengthen governance across financial institutions.HealthcareSecure access to critical systems, patient data, and clinical environments.Federal & PublicSupport secure access, compliance, and operational resilience across public sector enterprises.Energies & Critical InfrastructureProtect critical systems and privileged access across essential infrastructure.EducationProtect your educational institution from ransomware and data misuse.VisibilityDiscover every human, machine, and AI identity across your environment.PostureIdentify excessive privileges, policy gaps, and emerging identity risks.ControlApply authorization and access policies to every identity, session, and action.Human IdentitiesSecure workforce, privileged, and third-party identities.Machine IdentitiesProtect secrets, credentials, certificates, and non-human identities.Agentic IdentitiesGovern and control access for AI agents and autonomous systems.Cloud StatusCheck availability and service health across Delinea cloud services.Customer SupportGet product support, technical guidance, and help from Delinea experts.Identity Security Maturity ModelAssess your identity security maturity and identify priorities for improvement.Professional ServicesAccelerate deployment, adoption, and value with expert implementation and advisory services.Trust CenterAccess Delinea security, privacy, compliance, and assurance information.User TrainingBuild product knowledge and skills with Delinea training and learning resources.
-
The Delinea PlatformA unified identity security platform that protects human, machine and AI identities across your enterprise.Delinea Iris AIAI-powered intelligence that delivers real-time insights, automation and continuous authorization.Secret ServerSecure privileged credentials with enterprise password vaulting and session management.Continuous Identity DiscoveryContinuously discover and inventory every identity across your enterprise.Credential ManagerManage, rotate and protect privileged credentials across hybrid and cloud environments.Fastpath Access GovernanceAutomate access governance, segregation of duties and compliance reporting.Privilege Control for ServersEnforce least privilege and application control across Windows and Linux servers.Privileged Remote AccessProvide secure remote access for employees and third parties without exposing privileged credentialsFull Product ListingBrowse the complete Delinea product portfolio and find the right solution for your enterprise.Why Delinea FastpathDiscover how Delinea Fastpath helps enterprises govern access, reduce risk and strengthen compliance across critical business applications.Delinea Fastpath Access ControlIdentify Segregation of Duties conflicts and sensitive access risk within and across business applications.Delinea Fastpath Access ReviewAutomate user access reviews and generate clear, consistent audit evidence with less manual effort.Delinea Fastpath Change TrackingMonitor critical permission, configuration and data changes across business applications.Delinea Fastpath Access ProvisioningAutomate compliant access requests, approvals, provisioning and deprovisioning.Delinea vs CyberArkCompare Delinea and CyberArk to see how the platforms differ in identity security, deployment and ease of use.Delinea vs BeyondTrustExplore the key differences between Delinea and BeyondTrust across privileged access and identity security.Delinea vs MicrosoftSee how Delinea extends beyond native Microsoft capabilities to deliver comprehensive identity security.Delinea vs One IdentitySee how Delinea authorizes every action at runtime, keeps credentials off users and AI agents and supports your identity provider.Delinea vs SaviyntExplore how Delinea and Saviynt compare across identity security, governance and privileged access.
-
All ResourcesBrowse Delinea’s complete library of educational content and resources.BlogsStay up to date with the latest identity security insights and industry trends.VideosWatch product demonstrations, customer stories and educational content.WebinarsJoin expert-led webinars covering identity security and best practices.EventsDiscover upcoming conferences, webinars and Delinea events.EbooksDownload in-depth guides, research and educational resources.GlossaryUnderstand key identity security, cybersecurity, and privileged access terms with Delinea’s comprehensive glossary.PodcastEnjoy freshly brewed hot takes with our Grounds for Access podcast.Product DocumentationAccess technical guides, product documentation, and implementation resources.Solution BriefsLearn how Delinea solutions address specific business and security challenges.Trust CenterReview security, compliance, privacy, and trust-related information.
-
Customer SuccessMaximize the value of your Delinea investment with expert guidance and ongoing success planning.Professional ServicesAccelerate deployment and optimize your identity security strategy with Delinea experts.User TrainingBuild product knowledge and develop expertise through Delinea training and certification programs.Cloud StatusView the real-time status and availability of Delinea cloud services.Customer CommunityConnect with peers, share knowledge and discover best practices from the Delinea community.Integrations MarketplaceExplore integrations that extend and enhance the Delinea Platform across your technology ecosystem.Product DocumentationAccess technical documentation, product guides, APIs and implementation resources.Technical SupportGet expert assistance, troubleshoot issues and manage support requests.Trust CenterReview Delinea’s security, compliance, privacy and trust information.
-
About DelineaLearn about Delinea’s mission, vision, and approach to identity security.The Delinea DifferenceDiscover what sets Delinea apart in securing human, machine, and AI identities.Leadership TeamMeet the leaders driving Delinea’s strategy and innovation.Contact UsConnect with our teams around the world.
Privileged Access Management for Databases
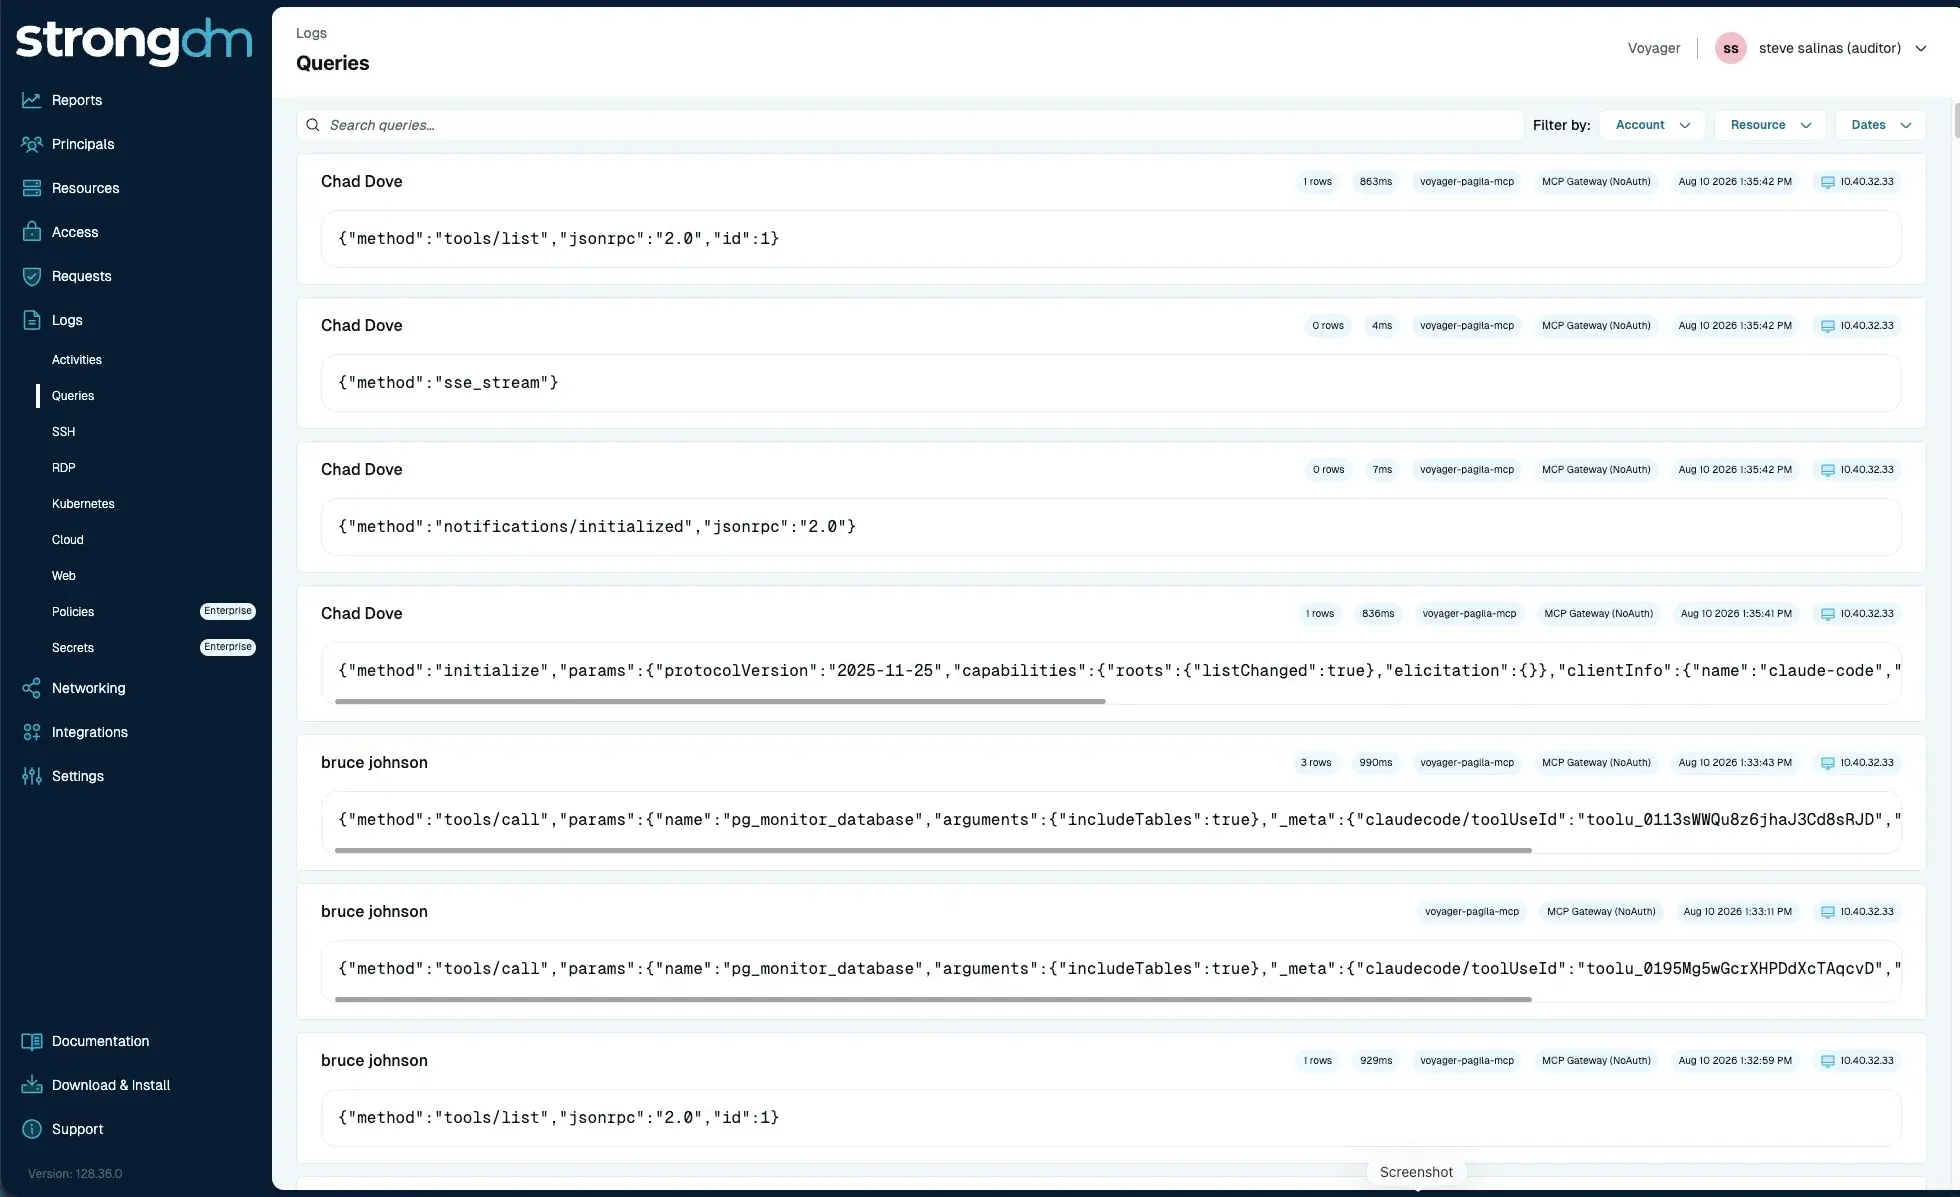
Every Query, Attributed to a Person, Not a Shared Login
Nobody on your team needs to know the database password.
Teams share database credentials more than any other credential type because rotating them is a hassle and revoking access for one person without breaking everyone else is worse. Delinea leases credentials at connection time and injects them at the proxy layer, so users never see the password and every query in the logs traces back to the person who ran it, not a generic shared account.
Rotate Credentials Without Breaking Access
Rotation stops being a change-management event.
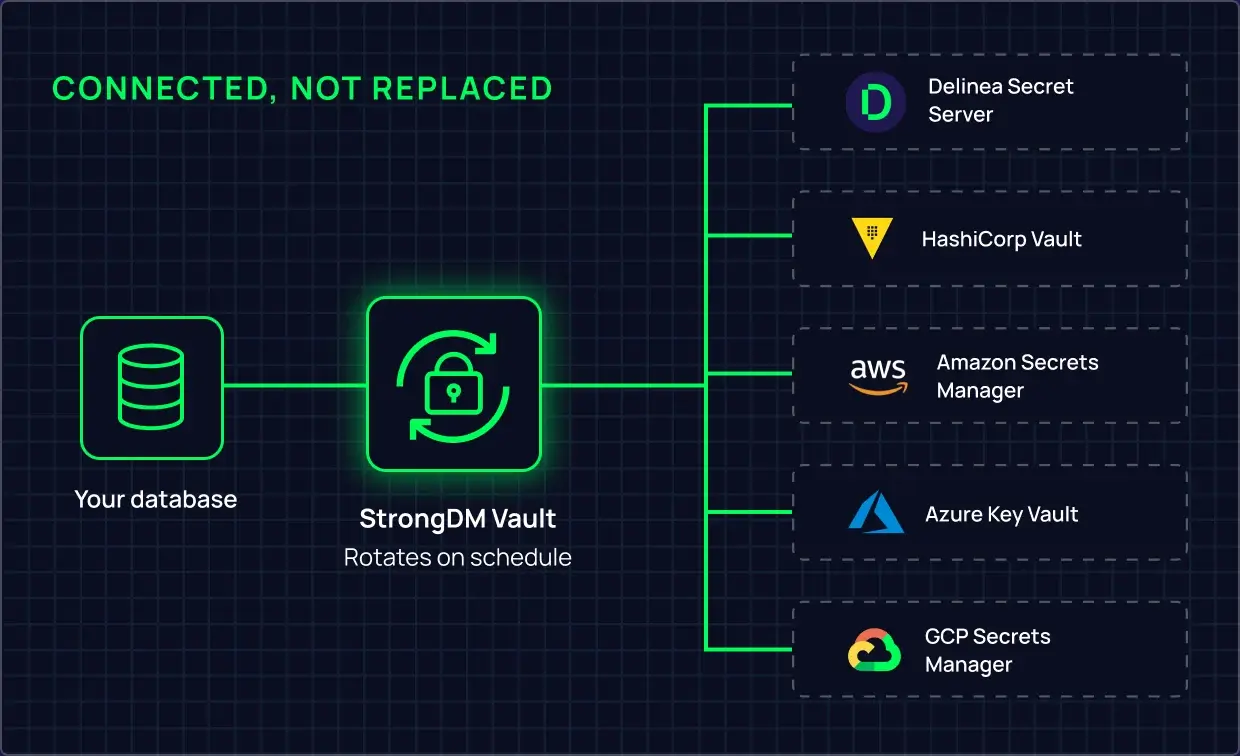
Delinea Vault rotates database credentials for PostgreSQL, MySQL, and SQL Server on a schedule. It updates the database and your secret store at the same time, so a rotation never leaves a stale password behind. If you already run Delinea Secret Server, HashiCorp Vault, AWS Secrets Manager, Azure Key Vault, or GCP Secret Manager, Delinea works with what you have instead of asking you to move your secrets.
Control What a Query Can Do, Not Just Who Can Connect
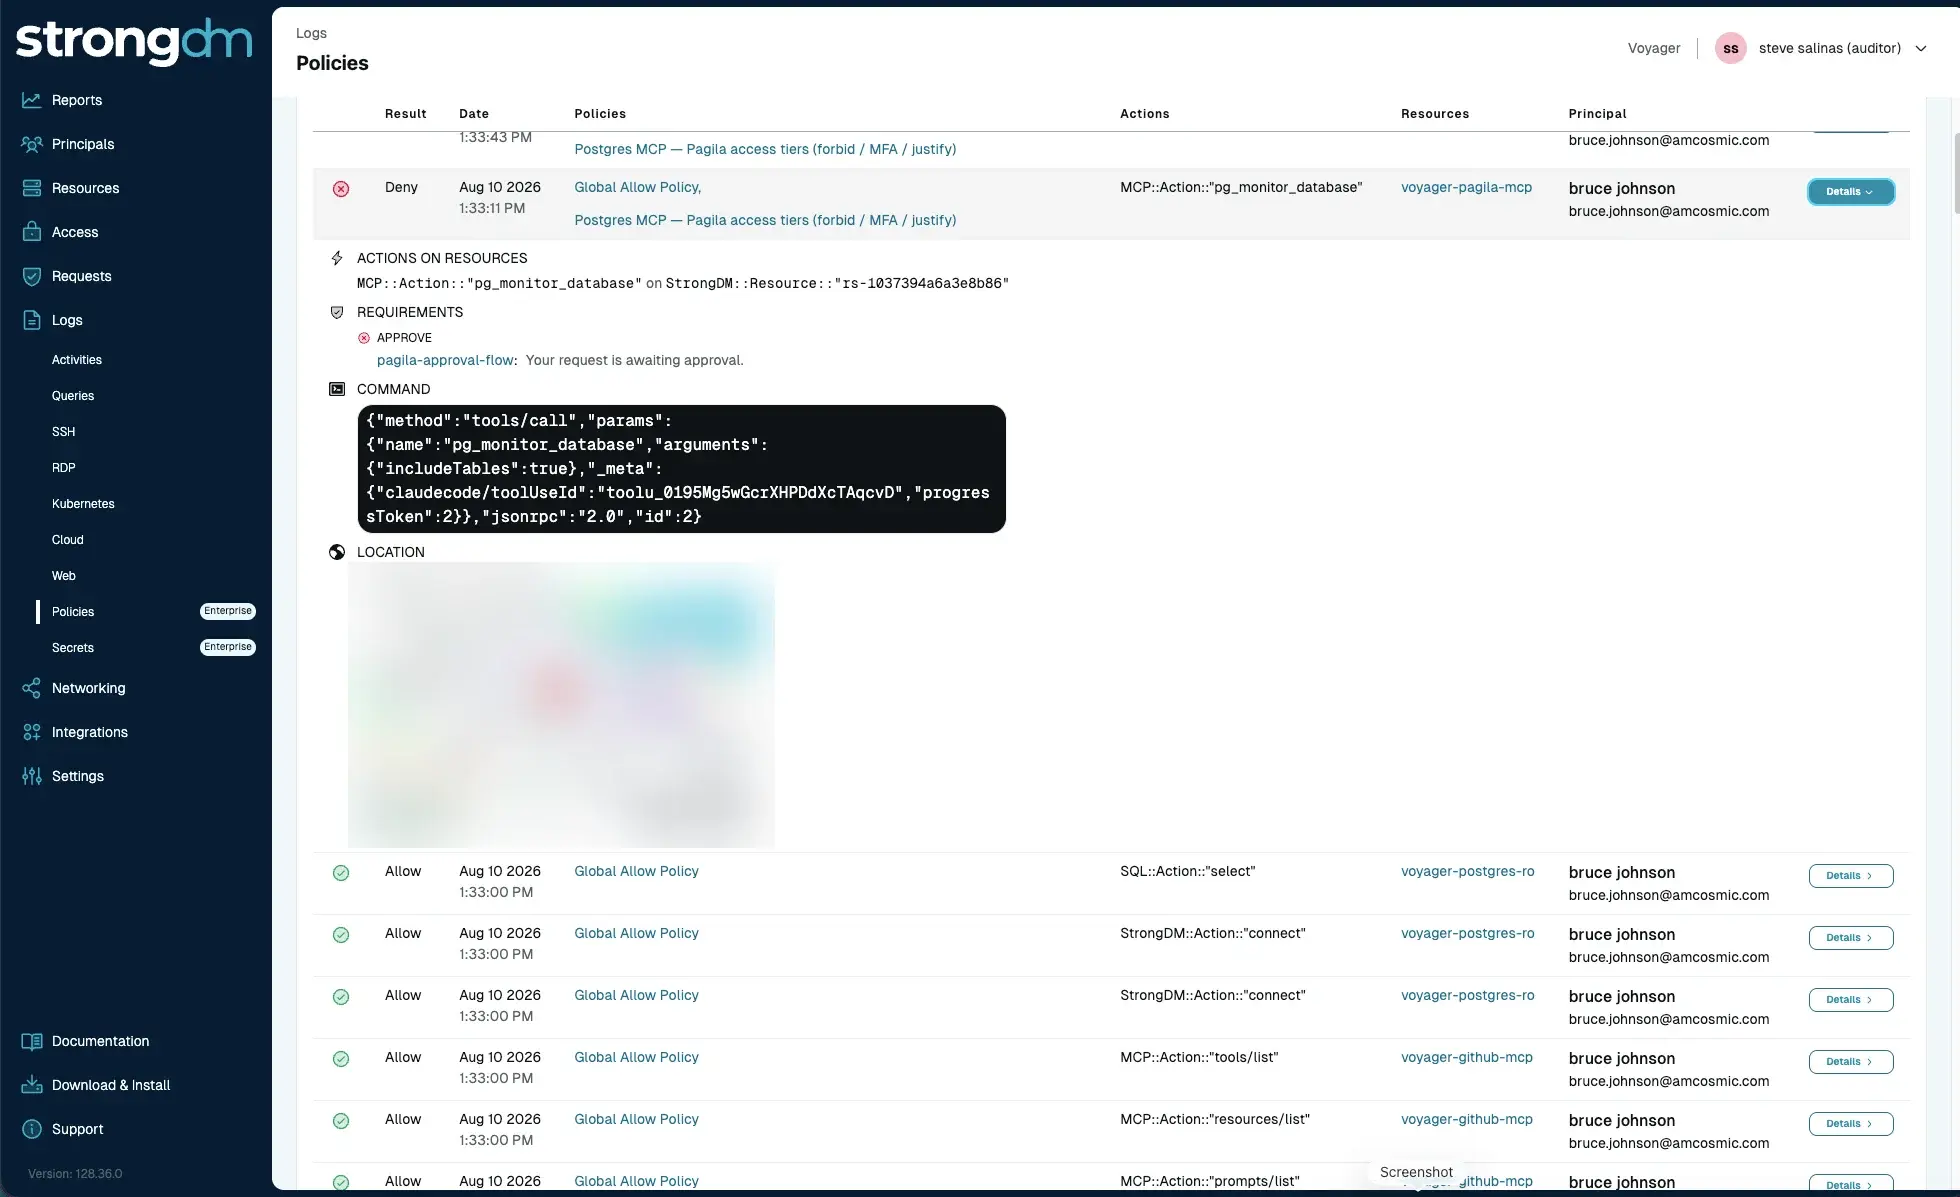
The rule that governs your production database governs the router in front Read access stays open. The destructive commands don’t.
Connecting to a database and dropping a table carry very different levels of risk, and most access tools govern only the first. Delinea’s policy engine supports action-level control for PostgreSQL and SQL Server, so you can leave read access open broadly and still block the handful of commands that would actually cause damage.
See Your Access Before an Auditor Does
Access you can show an auditor the day they ask.
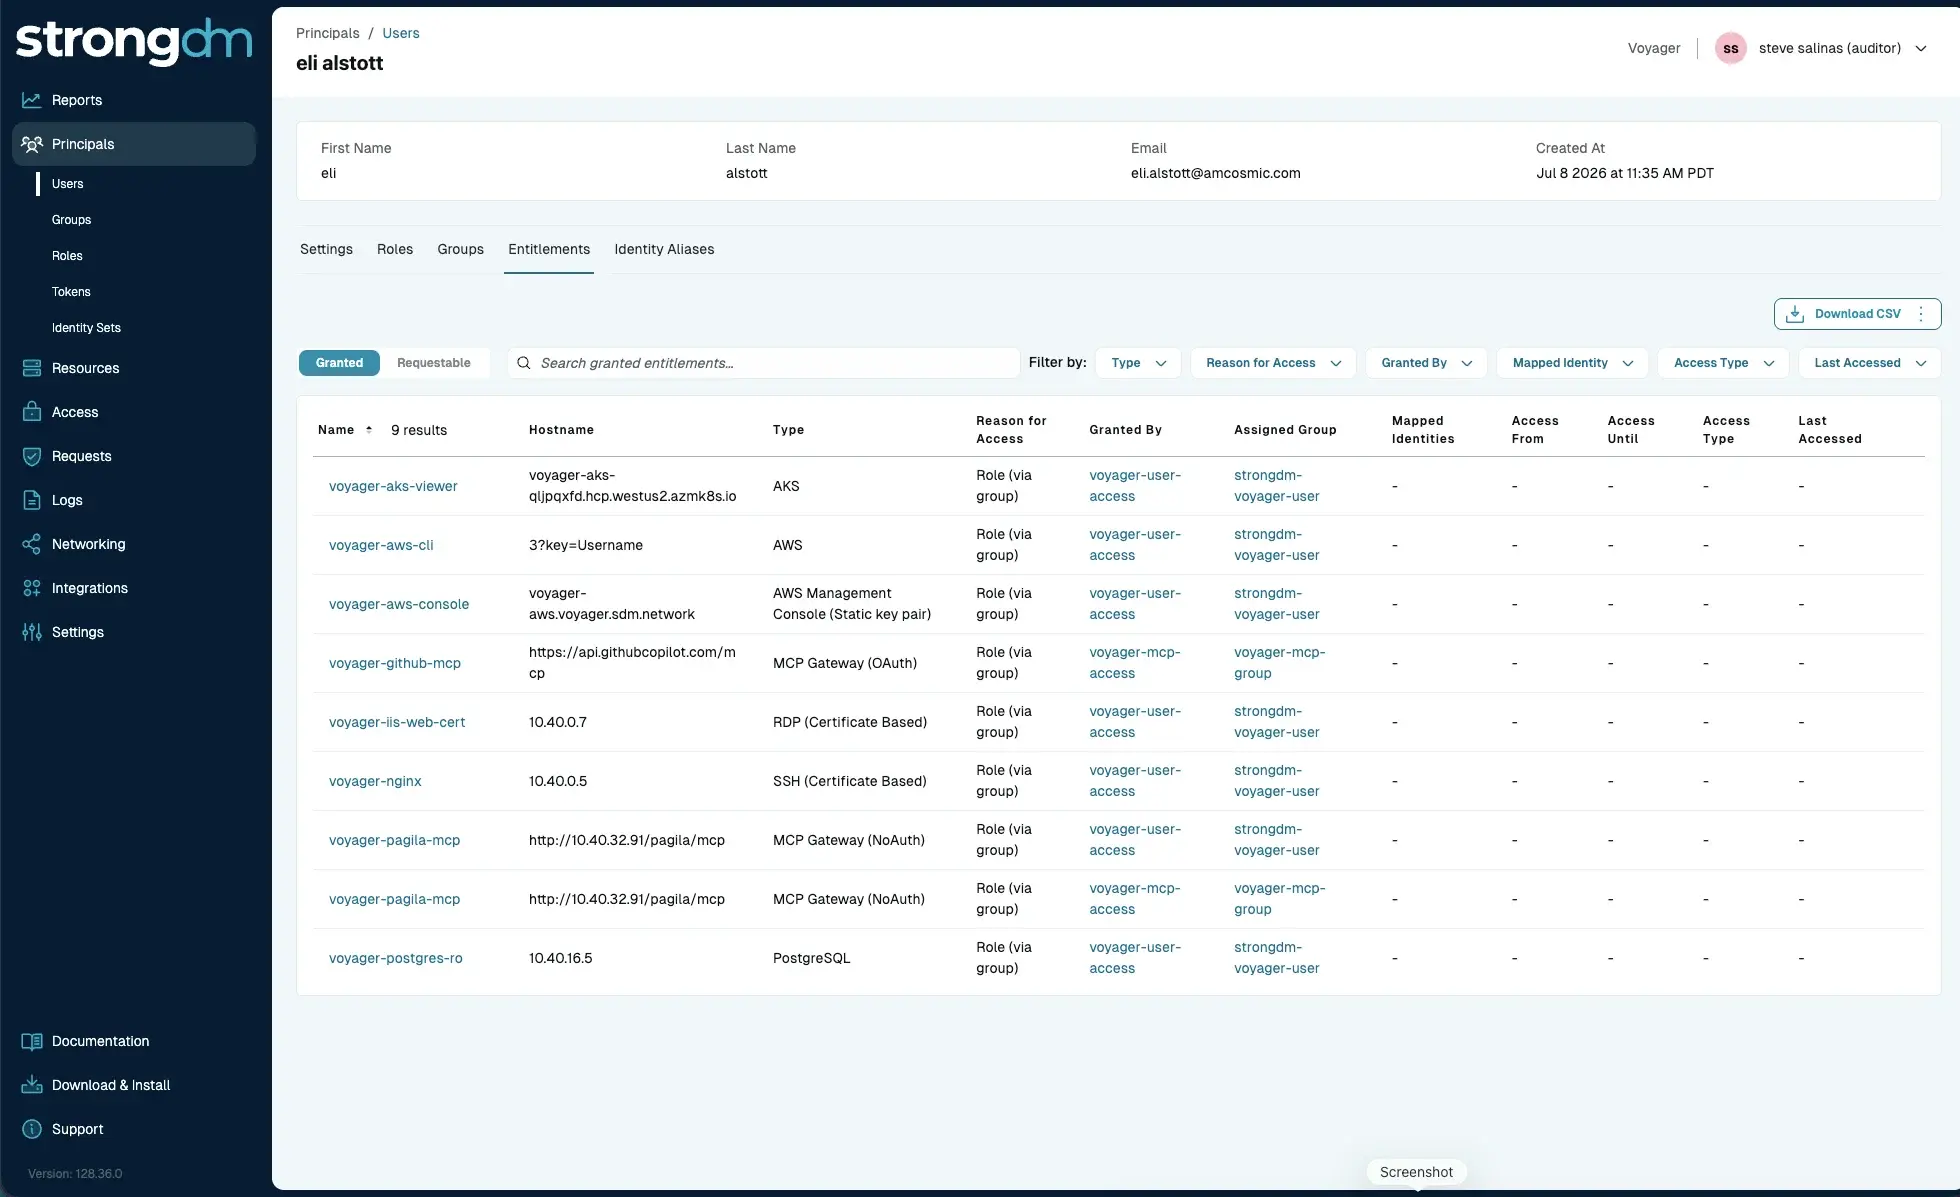
Most database access tools give you a wall of logs and nothing to act on. Delinea’s Entitlements Visibility and reporting dashboards show access across your databases and let you export compliance-ready reports on demand, so a SOC 2 or ISO 27001 audit starts from a report you already have instead of a project you have to start.
WHY DELINEABuilt for the Way Your Team Works
-
Compliance-ReadyWhen a review comes around, auditors get one trail that already includes network hardware, instead of a separate export from the network team.
-
Fits Around the Bastion You Already Run
Teams that route database access through a bastion host, or share a handful of DBA logins, can move resource by resource. Delinea sits in front of the database and takes over authentication and auditing without a full cutover.
-
Extends Your Existing PAM Investment
If you already vault and rotate database credentials with a tool like Delinea Secret Server, Just-in-Time adds query-level access control on top of that investment, rather than asking you to replace it.
“If someone is looking for a quick approach to secure how access is being provisioned and they want to make that maturity improvement very quickly, I would tell them to look at Delinea because of how easy it is to use and how easy it is to deploy and roll out. It will help them leapfrog the access improvements they need or want to make in their programs.”
Raghu Valipireddy SVP, Axos Financial
A Tailored Solution Just for Your Organization
Whether you’re running a single PostgreSQL instance or a dozen database engines across clouds, Delinea connects to the technology you already run. Delinea fits your environment. You don’t have to fit it.
What's trending in identity security
Don’t wait to extend and modernize your identity security. Reduce risk, eliminate silos, and scale with confidence.
Download the whitepaper
From mitigating data breach risks to enhancing compliance, these organizations share how Delinea’s Privileged Access Management (PAM) solutions addressed their pain points and delivered both financial and operational returns.
Download the report
Whether you’re new to PAM or updating an existing program, this guide helps you align privilege security with business needs—without getting bogged down in complexity.
Download the eBook